Skip to content

Santry · AI Agent Governance

Build trust in AI actions.

Clear identity. Defined permissions. Traceable actions.Let agents collaborate and act within the boundaries your enterprise sets.

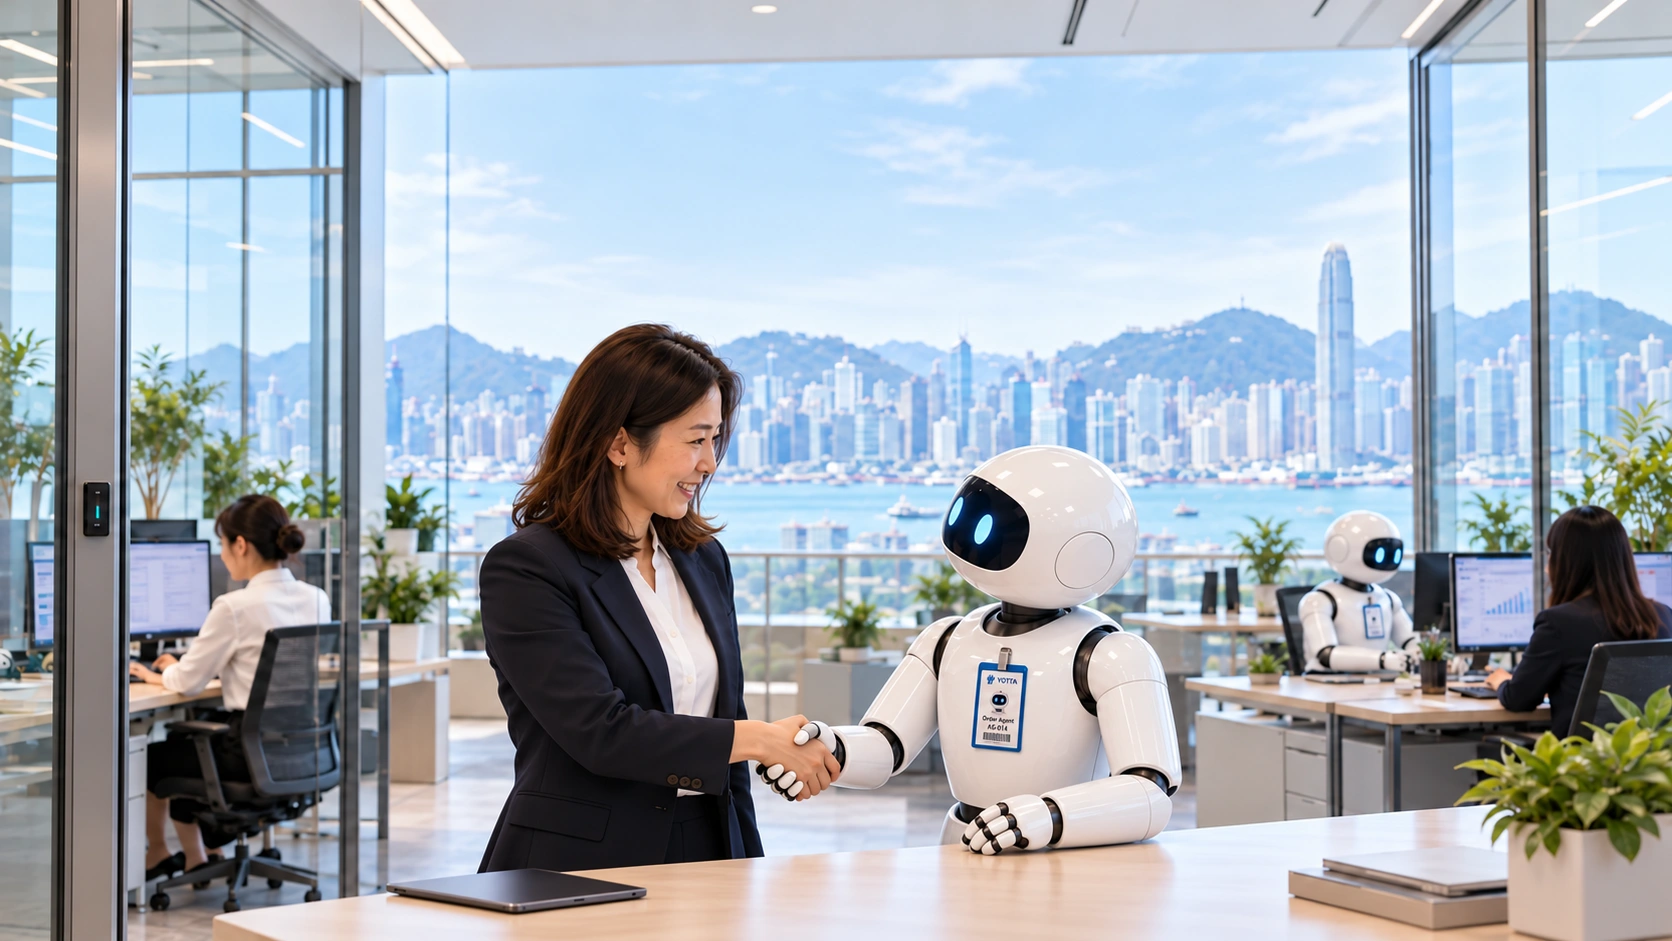
Illustrative workplace: a smiling manager and a badge-wearing Agent shake hands beside glass-partitioned work areas, while colleagues and another Agent work nearby.

Why governance matters

Before agents act, answer three questions.

  • Who is acting?

    A task can pass between agents. The original requester and the responsible team need to stay identifiable.

  • What is approved this time?

    Access to a system does not authorize every action. A specific payment or data change needs its own authorization.

  • Can we explain what happened?

    When requests, approvals and system results live in separate places, reconstructing an operation becomes difficult.

How Santry works

Create and manage agent identities centrally. Define permissions and responsibilities clearly.

Santry gives every agent a distinct identity and connects access permissions, action authorization, and activity records, so your organization can see who is acting, what they are authorized to do, and the outcome.

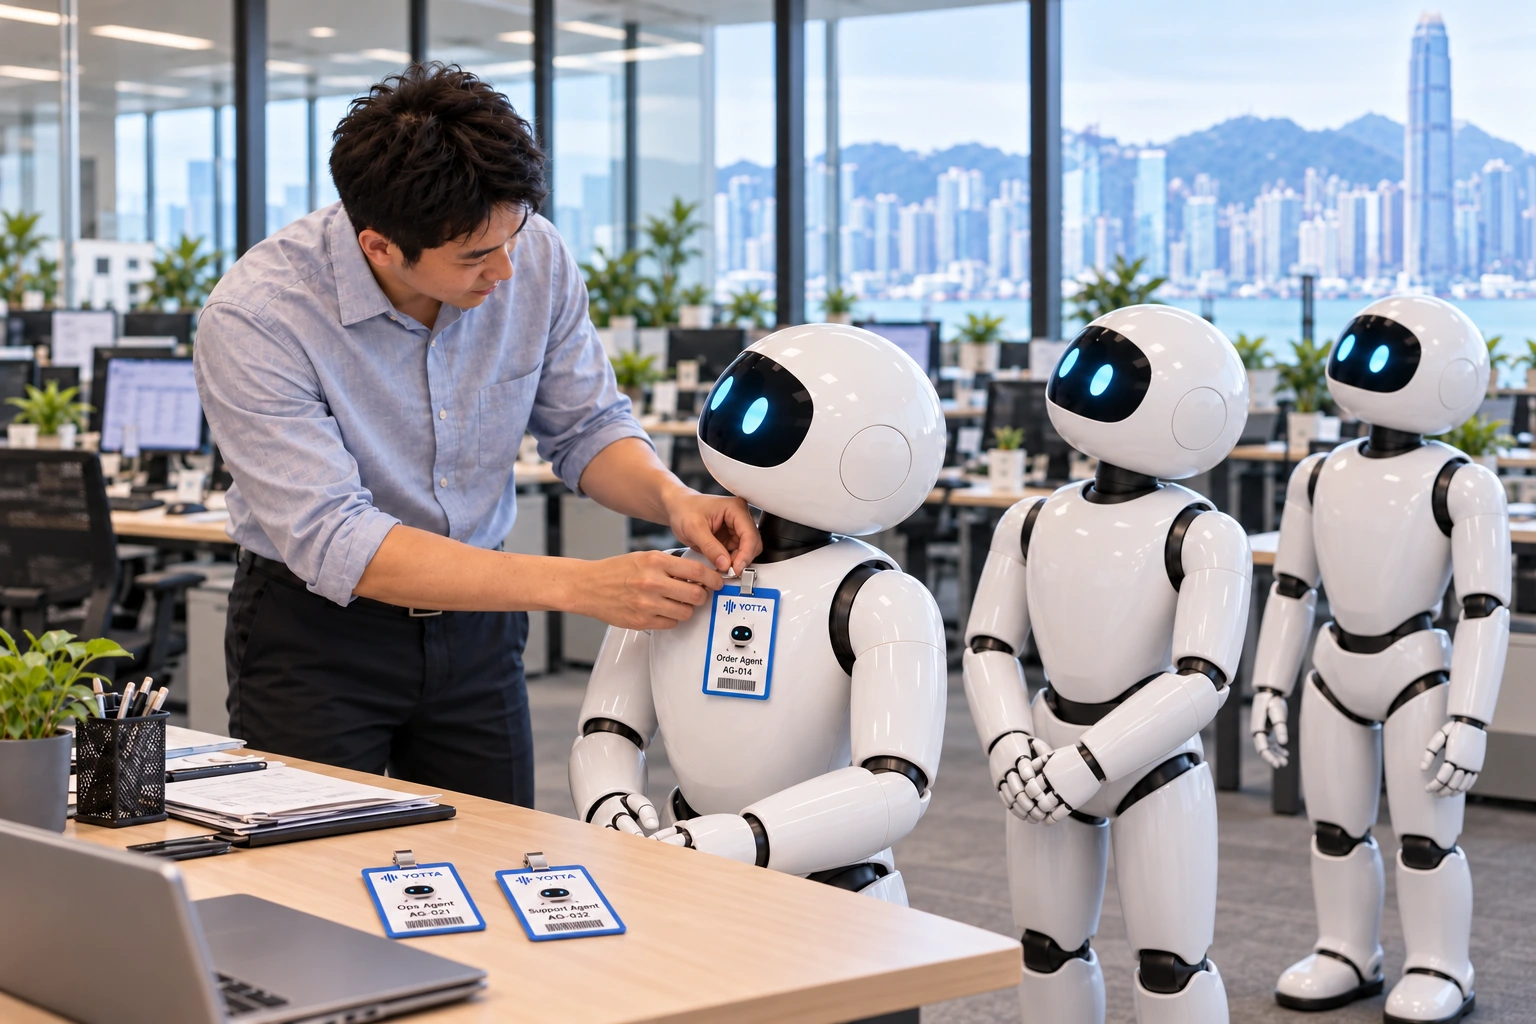
An engineer in a pale blue shirt clips a badge to the Order Agent at the front of a queue, while two other robots representing software agents wait to receive their own identity badges

01 / Get a badge

Establish a trusted identity for every agent.

Santry registers each agent, issues a dedicated identity credential, and records its team, responsibilities, and accountable owner. By linking to your existing enterprise identity system, Santry gives every agent a clear identity and an accountable owner.

Identify both the person making the request and the agent carrying it out.
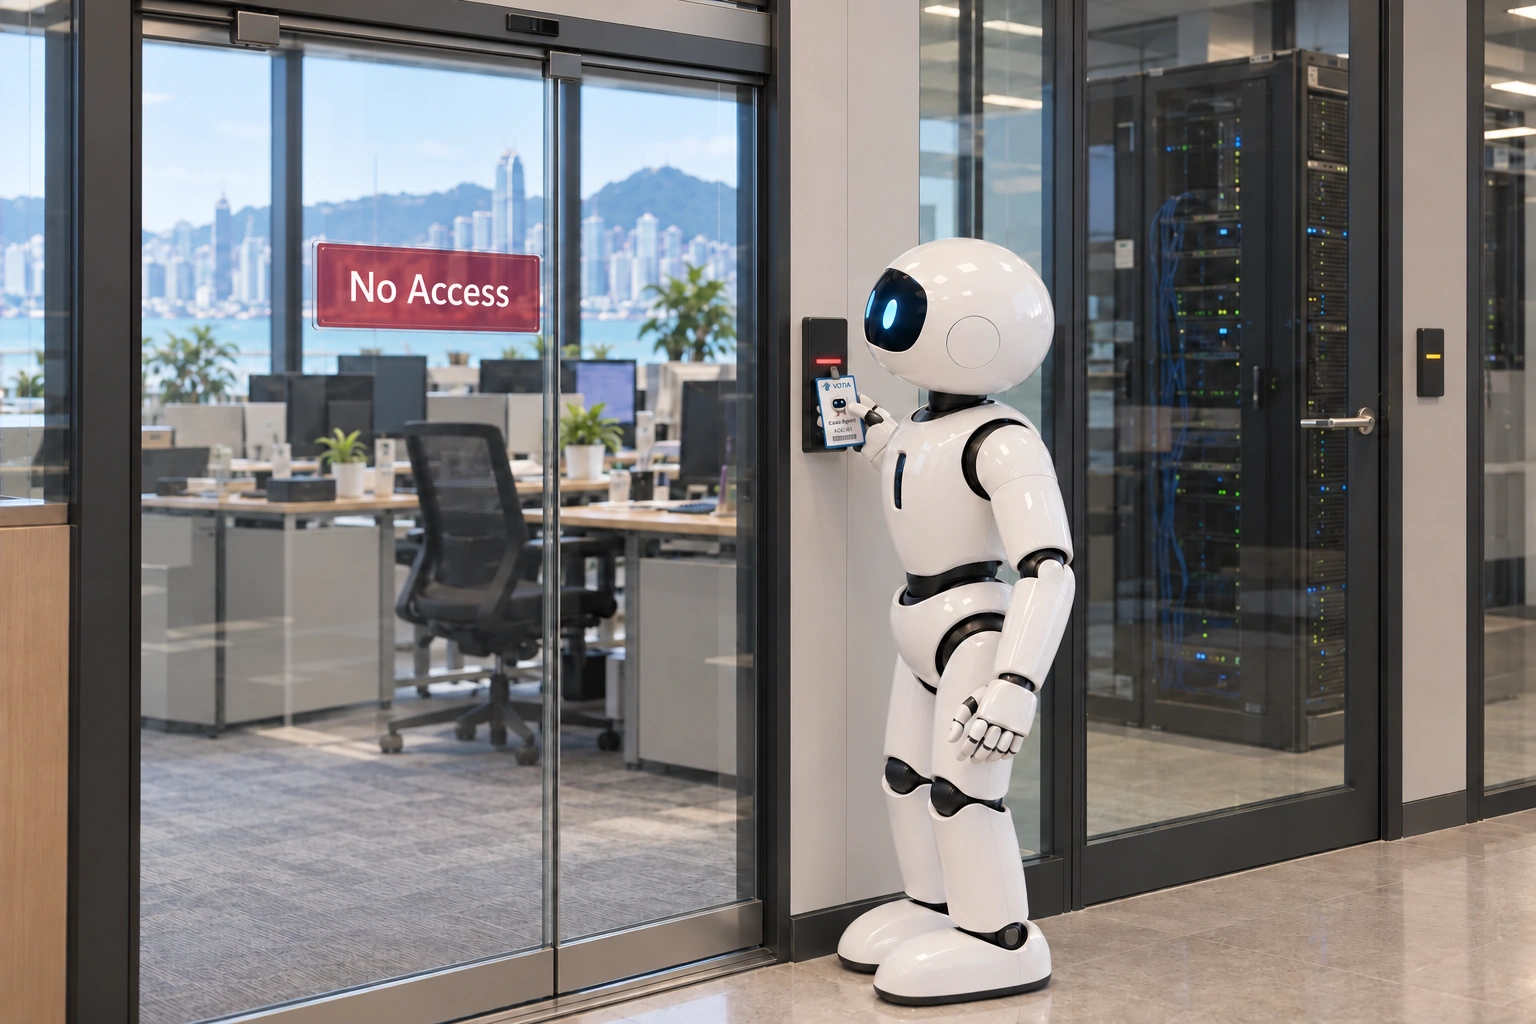
The Agent remains outside a closed sliding glass door displaying No Access, with a red light on the badge reader

02 / Check access

You decide what agents can do.

Santry checks an agent's access to tools, systems, and environments against your organization's rules. Only authorized resources are accessible; unauthorized requests are blocked by default, keeping collaboration within clear boundaries.

When a task passes between agents, each agent must independently pass permission checks, with the original request's source preserved. Collaboration can continue without expanding permissions.

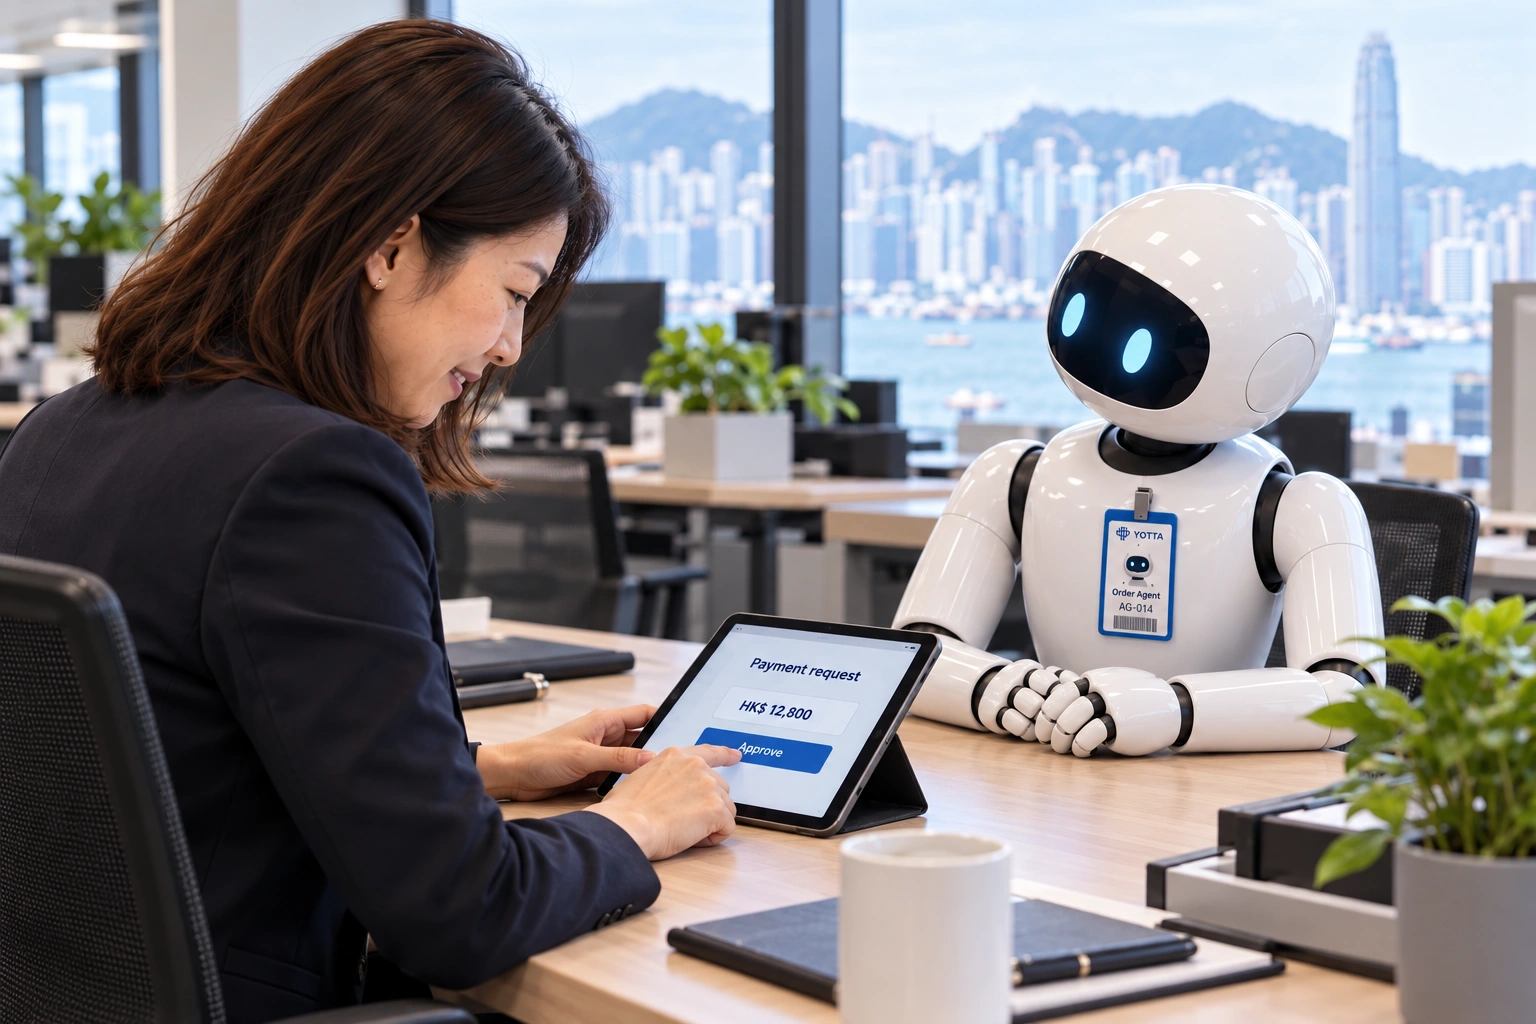
The manager in a navy suit is seen from the side reviewing a payment request on a tablet facing her, while the Agent waits beside her

03 / Act within authorization

Critical actions need approval. Santry verifies before execution.

Santry identifies critical actions according to your organization's rules and routes requests to the responsible person for approval. Once approved, Santry checks that the authorization is valid and matches the action's details and scope. Only then can the agent proceed.

The badge represents identity and standing access permissions. Action authorization is limited to the particular operation and target approved this time.

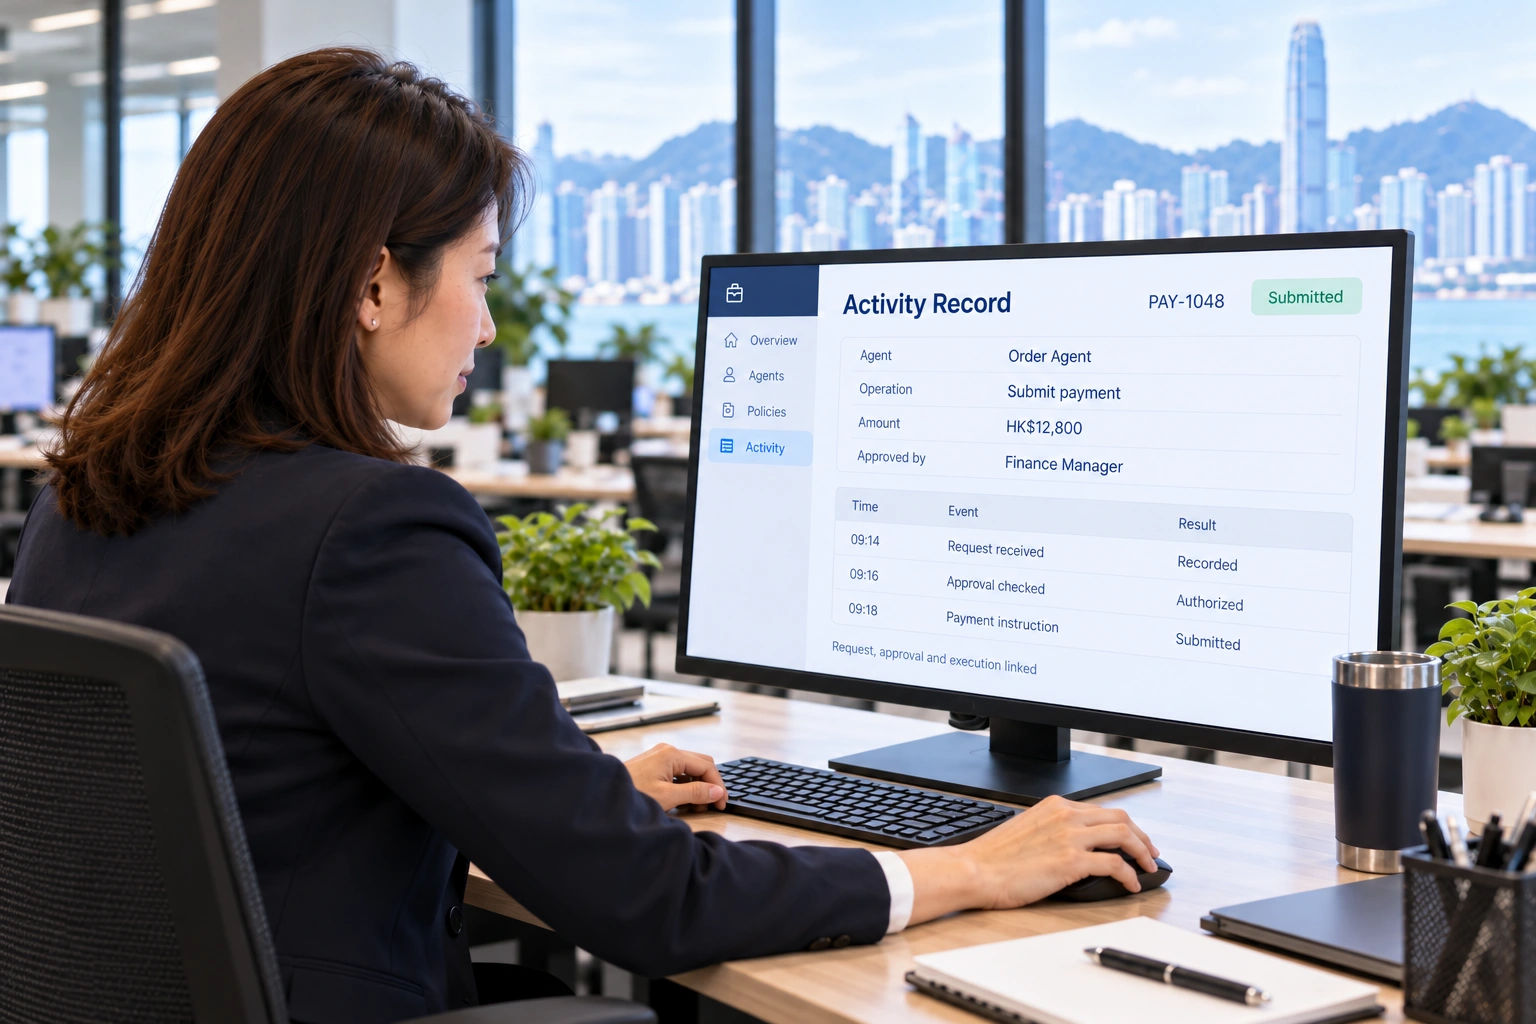
Viewed from behind and to the side, the manager reviews a detailed Activity Record on a large monitor facing her, with her right hand on the mouse

04 / Review the record

Make every agent action traceable.

Santry connects each action's request source, authorization basis, and execution result. It records who initiated the request, who approved it, which agent carried it out, and the outcome, providing evidence for ongoing oversight, compliance reviews, and accountability.

Follow the original request through to the returned result, with evidence for investigation and business review.

Santry in practice

How does Santry govern this HK$12,800 payment?

Apply the story's identity, access, action authorization, and records to this HK$12,800 payment. Simulate an account change to see where Santry stops the action.

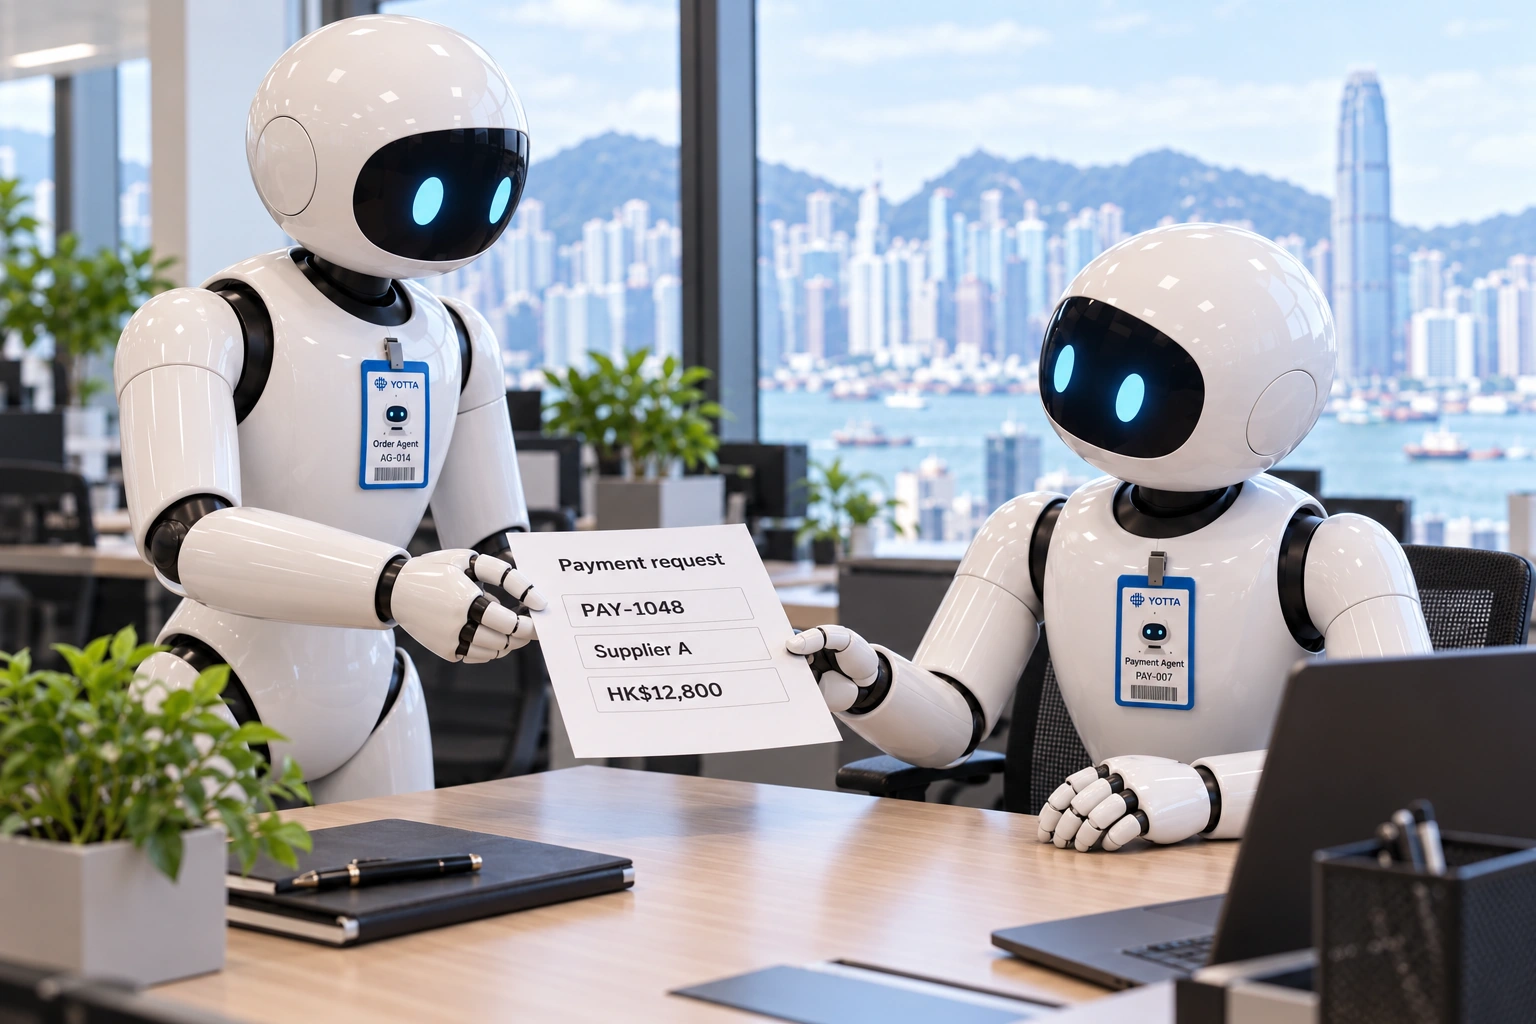
Order Agent AG-014 hands payment request PAY-1048 for HK$12,800 to Payment Agent PAY-007. Both agents wear distinct identity badges.
One request, two identified agents: prepare the application, then hand it over.

Who is handling this request?

A procurement colleague requests payment. The finance assistant prepares the application, and a separate payment agent handles execution.

From the story: 01 · Receive a badge
Supplier payment demonstration

Payment request PAY-1048

Identity linked
Amount
HK$12,800
Recipient
Supplier A
Requested account
•••• 4821

People and agents in this request

  • Requester

    Procurement colleague

  • Finance assistant

    Order Agent

    AG-014
  • Payment execution

    Payment Agent

    PAY-007

Agent owner teamFinance team

Handover keeps the original request linked. The receiving agent's identity and permissions are checked again.

What if the account changes?

Keep the approval for 4821, but change the instruction to 9067.

A business demonstration of the workflow, not the actual product interface or a customer case. Records shown cover operations governed through Santry.

Working with your systems

Connect to the workplace you already have.

Start with the agents, tools, and workflows your team already uses.

Connections at a glance

Your agents

Calls & handoffs

Santry

Permission checks

Activity records

Tools & systems

MCP tools

Business services

Your enterprise processes

Enterprise identity

Approval workflows

Illustration of connections governed through Santry.

Connect your agents and tools

Connect existing agents, MCP tools, and business services. Santry checks permissions for the calls and task handoffs that pass through it.

Keep your identities and approvals

Keep your enterprise identities and approval workflows. Business systems continue to enforce their own permission checks.

Deploy to suit your environment

On-premise

Deploy and operate Santry in your own environment.

SaaS

Use the hosted service and reduce infrastructure maintenance.

For technical teams: view the platform architecture

How Console, Registry, Policy, and AgentGateway support the governed request path.

Request origin

Business user
Orchestrator agent
Specialist agent

Original intent + caller context

Santry governance

Console

Configure agents and governance

Registry

Find agents & services

Policy

Evaluate access & task scope

AgentGateway

Verify · decide · route

Connected environment

Agent services
Business applications
Enterprise data

Only within the authorized scope

A connected audit trail

Original request · participating agents · authorization decision · execution context

Conceptual platform architecture. Connections and deployment are defined for your environment.

Start with a single workflow.

Choose a workflow and verify that permitted actions proceed, unauthorized actions are stopped, and approval records can be reviewed. Then extend the proven rules and connections to more teams.

Discuss a Santry demo

Before your pilot

What should we prepare for a pilot?

Bring one workflow, the agents and tools involved, and your current permission and approval rules. Together, we can identify the actions that should proceed, the ones that should be blocked, and the records needed for review.

Does every action require human approval?

No. Routine tasks can run automatically under your enterprise rules. Sensitive actions, such as payments or data changes, follow your existing approval process.